
Linking Talend Administration Center in SP-initiated mode with Keycloak
Last updated: 10/9/2026
These steps are performed on Talend Administration Center
tab.
About this task
Some screenshots in this article show the Keycloak admin console used when this procedure was created in June 2022. In later Keycloak releases, some labels and page locations can differ.
Procedure
-
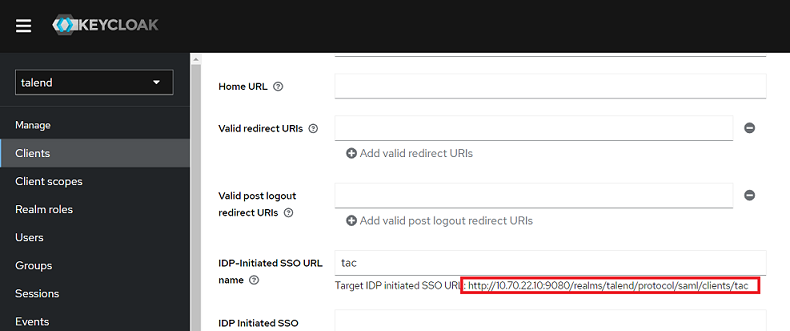
In the Service Provider Entity URL field, enter the
Talend Administration Center SSO Service URL.
To find this URL, go to your Keycloak realm account and open the Clients tab.
-
If you want to sign the logout request, add the following properties to the
configuration.properties file.
Property Description Default/supported values sso.signature.key.name Defines the key identifier type used to sign the SAML logout request. Default value is NONE. Supported values are NONE and KEY_ID. sso.signature.key.path Specifies the path to the private key used to sign the SAML logout request. This property is empty by default. sso.signature.certificate.path Specifies the path to the certificate associated with the private key used to sign the SAML logout request. This property is empty by default. sso.signature.algorithm Specifies the signature algorithm used to sign the SAML logout request. Default value is http://www.w3.org/2001/04/xmldsig-more#rsa-sha256.
Supported values are http://www.w3.org/2001/04/xmldsig-more#rsa-sha256, http://www.w3.org/2001/04/xmldsig-more#rsa-sha384, and http://www.w3.org/2001/04/xmldsig-more#rsa-sha512.
The signature-related parameters must match the Keycloak configuration.

-
If you don't want to sign the logout request, you must toggle off the following
settings from the Clients page in Keycloak.
- Sign documents option under Signature
and Encryption in the Settings tab

- Client signature required option under
Signing keys config in the
Keys tab

If these options are not disabled, the unsigned SAML logout request will fail. - Sign documents option under Signature
and Encryption in the Settings tab