
Configuring Talend Administration Center in IdP-initiated mode with Keycloak
Last updated: 10/6/2026About this task
The screenshots in this article show the Keycloak admin console used when this procedure was documented in June 2022. In later Keycloak releases, some labels and page locations can differ.
Procedure
-
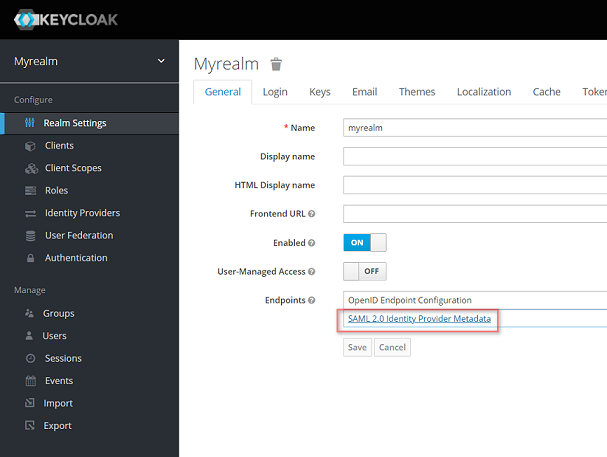
On Keycloak web platform, download the Keycloak IDP metadata
file from the Realm Settings page.
-
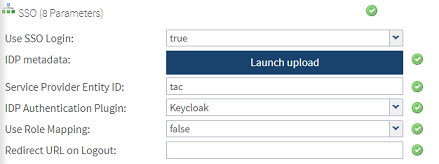
Set the parameters as follows:
Field Description Use SSO login Select true if SSO has not been enabled yet. IDP metadata Click Launch upload to upload the metadata file you have previously downloaded from the Keycloak system. Service Provider Entity ID Enter the Keycloak "Client ID", in this example tac. IDP Authentication Plugin Select Keycloak. Identity Provider Configuration Enter the Keycloak administrator user name and password required by the configured realm and client connection for user synchronization. In some versions, TAC can label the password field as a token field. Enable SSO user sync Set the value to true to enable scheduled synchronization of SSO-managed users for this Keycloak configuration. Sync interval Enter a positive integer. The default value is 60 minutes. Use Role Mapping Select one of the following options: - true: login to TAC from the identity provider
will create/update users with Talend Administration Center roles, attributes name: firstName,
lastName, email,
tac.projectType, tac.role.
For more information, see Configuring Role Mapping.
- false: no attributes are obtained from the identity provider, but with the default Security Administrator user that was created earlier, you can assign Talend Administration Center roles to other users created by the identity provider.
Redirect URL on Logout Enter the URL of the Keycloak page to open after users log out of Talend Administration Center. If this field is empty, the browser is redirected to the default location of Talend Administration Center after logout.
During each sync, Talend Administration Center checks the users available for the configured Keycloak realm and client and sets SSO-managed users to inactive when they are no longer present. On the first SSO login, an existing Talend Administration Center user becomes SSO-managed. A successful SSO login reactivates an inactive SSO-managed user.
- true: login to TAC from the identity provider
will create/update users with Talend Administration Center roles, attributes name: firstName,
lastName, email,
tac.projectType, tac.role.